

The short answer
A white hat hacker is a security professional who uses hacking skills with the system owner's permission to find and fix weaknesses, usually as a penetration tester or bug bounty researcher. A black hat hacker breaks in without permission for gain or harm. A grey hat hacks without permission, but usually without malicious intent.
On this page
A white hat hacker is a security specialist who hacks computer systems with the owner’s permission, to find weaknesses and get them fixed before criminals exploit them. Most work as penetration testers, in-house security staff or bug bounty researchers, and the role is also called ethical hacking.
The label comes from old Western films, where the heroes wore white hats and the villains wore black. In cyber security the colour stands for one thing above all: whether the hacker has permission. This entry is part of our cyber security glossary.
What is an ethical hacker?
An ethical hacker is a security professional who uses the same tools and techniques as criminal hackers, but with the system owner’s written permission, to find weaknesses so they can be fixed. “Ethical hacker” and “white hat hacker” mean the same thing: ethical hacker is the more common job title, and most ethical hackers work as penetration testers, red teamers or bug bounty researchers.
What makes the hacking ethical is the agreement around it rather than the techniques: permission from the owner, an agreed scope, care not to cause harm, and private reporting of everything found. If you need one for your own systems, see how do you hire a white hat hacker? below, or our penetration testing services.
What is the difference between white hat, black hat and grey hat hackers?
The difference is authorisation and intent. A white hat has permission, a black hat has neither permission nor good intent, and a grey hat acts without permission but usually without malice.
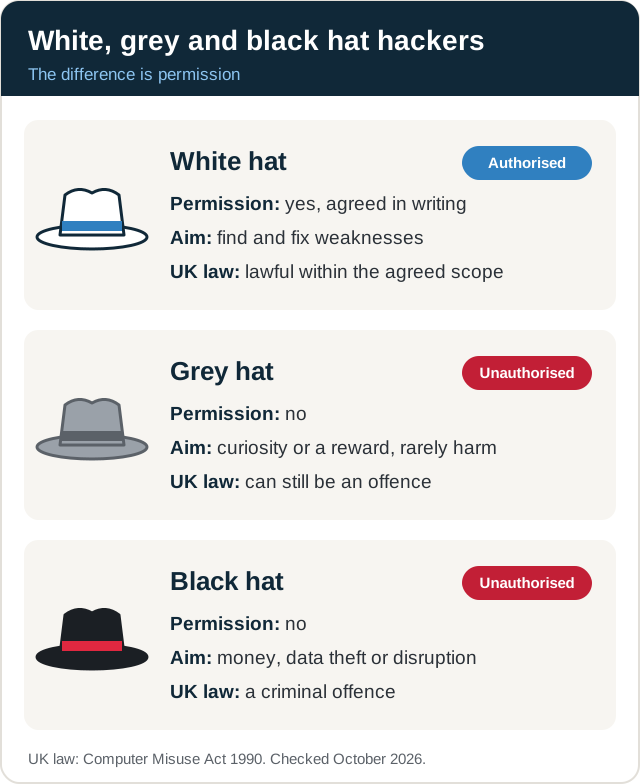
The table compares the types of hackers you will see named by hat colour, including the less common red and blue hats:
| Type | Permission from the system owner | Typical motive | What happens to findings | UK legal position |
|---|---|---|---|---|
| White hat | Yes, agreed in writing | Find and fix weaknesses | Reported privately to the owner | Lawful within the agreed authorisation |
| Grey hat | No | Curiosity, recognition or a reward after the fact | Often told to the owner, sometimes published or offered for payment | Can be an offence under the Computer Misuse Act 1990 |
| Black hat | No | Money, data theft, disruption or espionage | Exploited, sold or used for extortion | An offence under the Computer Misuse Act 1990, often alongside other crimes |
| Red hat | No | Stopping black hats, often by attacking their systems in return | Used to disrupt or take down criminal infrastructure | Still unauthorised access, so it can be an offence whatever the target |
| Blue hat | Usually yes, as an invited outside tester | Finding flaws in a product before it launches | Reported to the vendor | Lawful within the agreed authorisation |
Typical white hat roles are penetration tester, red teamer and researcher in a disclosure programme; typical black hats are ransomware operators, fraudsters and data thieves. Red and blue hat meanings vary from source to source: “blue hat” is also used for someone hacking out of revenge, which is an offence like any other unauthorised access, and “green hat” usually means a beginner still learning. Don’t confuse any of these with red and blue teams, which are defined roles in security testing: the red team plays the attacker with permission and the blue team defends. Our guide to red teaming explains how those exercises run.
How do white hat hackers work?
They work inside an agreed authorisation. Before testing starts, a professional engagement fixes five things in writing:
- Who authorises it. Someone with authority over the systems signs the approval. Where a cloud or hosting provider runs the systems, its testing rules apply too.
- Scope. The exact addresses, applications, accounts or sites that may be tested, and anything excluded.
- Rules of engagement. Test windows, techniques that are off limits (such as denial of service), emergency contacts and how to stop the test.
- Data handling. How any data seen during testing is protected, kept and deleted.
- Reporting. Findings go to the client in a report with severity ratings and fixes, not to the public.
That structure is what separates a penetration test from an attack: the techniques can be the same, but the permission differs. White hats also work through vulnerability disclosure and bug bounty programmes, where an organisation publishes what researchers may test and how to report. The NCSC’s vulnerability disclosure toolkit helps organisations set one up.
Is white hat hacking legal in the UK?
Yes, when the owner has authorised it and the hacker stays within that authorisation. Without permission, it can be a criminal offence. Section 1 of the Computer Misuse Act 1990 makes it an offence to make a computer perform any function intending to secure access you know is unauthorised. Motive is irrelevant, so a grey hat who breaks in “to help” can commit the same offence as a criminal.
The Act also makes it an offence to:
- gain unauthorised access intending to commit further offences (section 2);
- carry out unauthorised acts that impair a computer, such as deleting data or disrupting a service (section 3);
- make, supply or obtain tools for use in computer misuse offences (section 3A).
The Act has no public-interest defence for security research. The government’s King’s Speech 2026 briefing notes (13 May 2026) say a proposed National Security Bill will update the Act, partly to help security professionals protect systems, but they do not set out a defence. As of October 2026 the Act contains none, so test only systems you own, systems you are authorised in writing to test, or systems covered by a published disclosure programme, and follow its rules.
How do you hire a white hat hacker?
Commission a penetration test from a firm that agrees scope, authorisation and reporting in writing. Ask who will test, how findings are rated and reported, and how your data is handled. Our guide to choosing a penetration testing company lists the questions to ask, and our penetration testing services page shows the tests we run.
Be wary of anyone who contacts you uninvited about a weakness and wants payment before explaining it. Treat it as a possible incident and check the claim with your own security provider.
Why Sovereign Secure
Our testers work as white hats under written authorisation and agreed rules of engagement. We test web applications, APIs, networks, cloud, mobile apps, hardware and IoT, wireless, AI and LLM systems and source code, and run social engineering, red team and vulnerability scanning work. Sovereign Secure is a PCI SSC Qualified Security Assessor company and ISO 27001 certified. To scope a test, request a penetration testing quote.
Your next step
- Scope your testChoose your test types and asset counts online to scope your penetration test.Scope your test
- Pen testing cost guideUK day rates, price ranges by test type and what drives the cost.Read the cost guide
- Talk to a testerTell us what you need tested. We aim to reply within one working day.Talk to a tester
Last reviewed October 2026 by the Sovereign Secure assessment team.














